AWS EKS Foundation
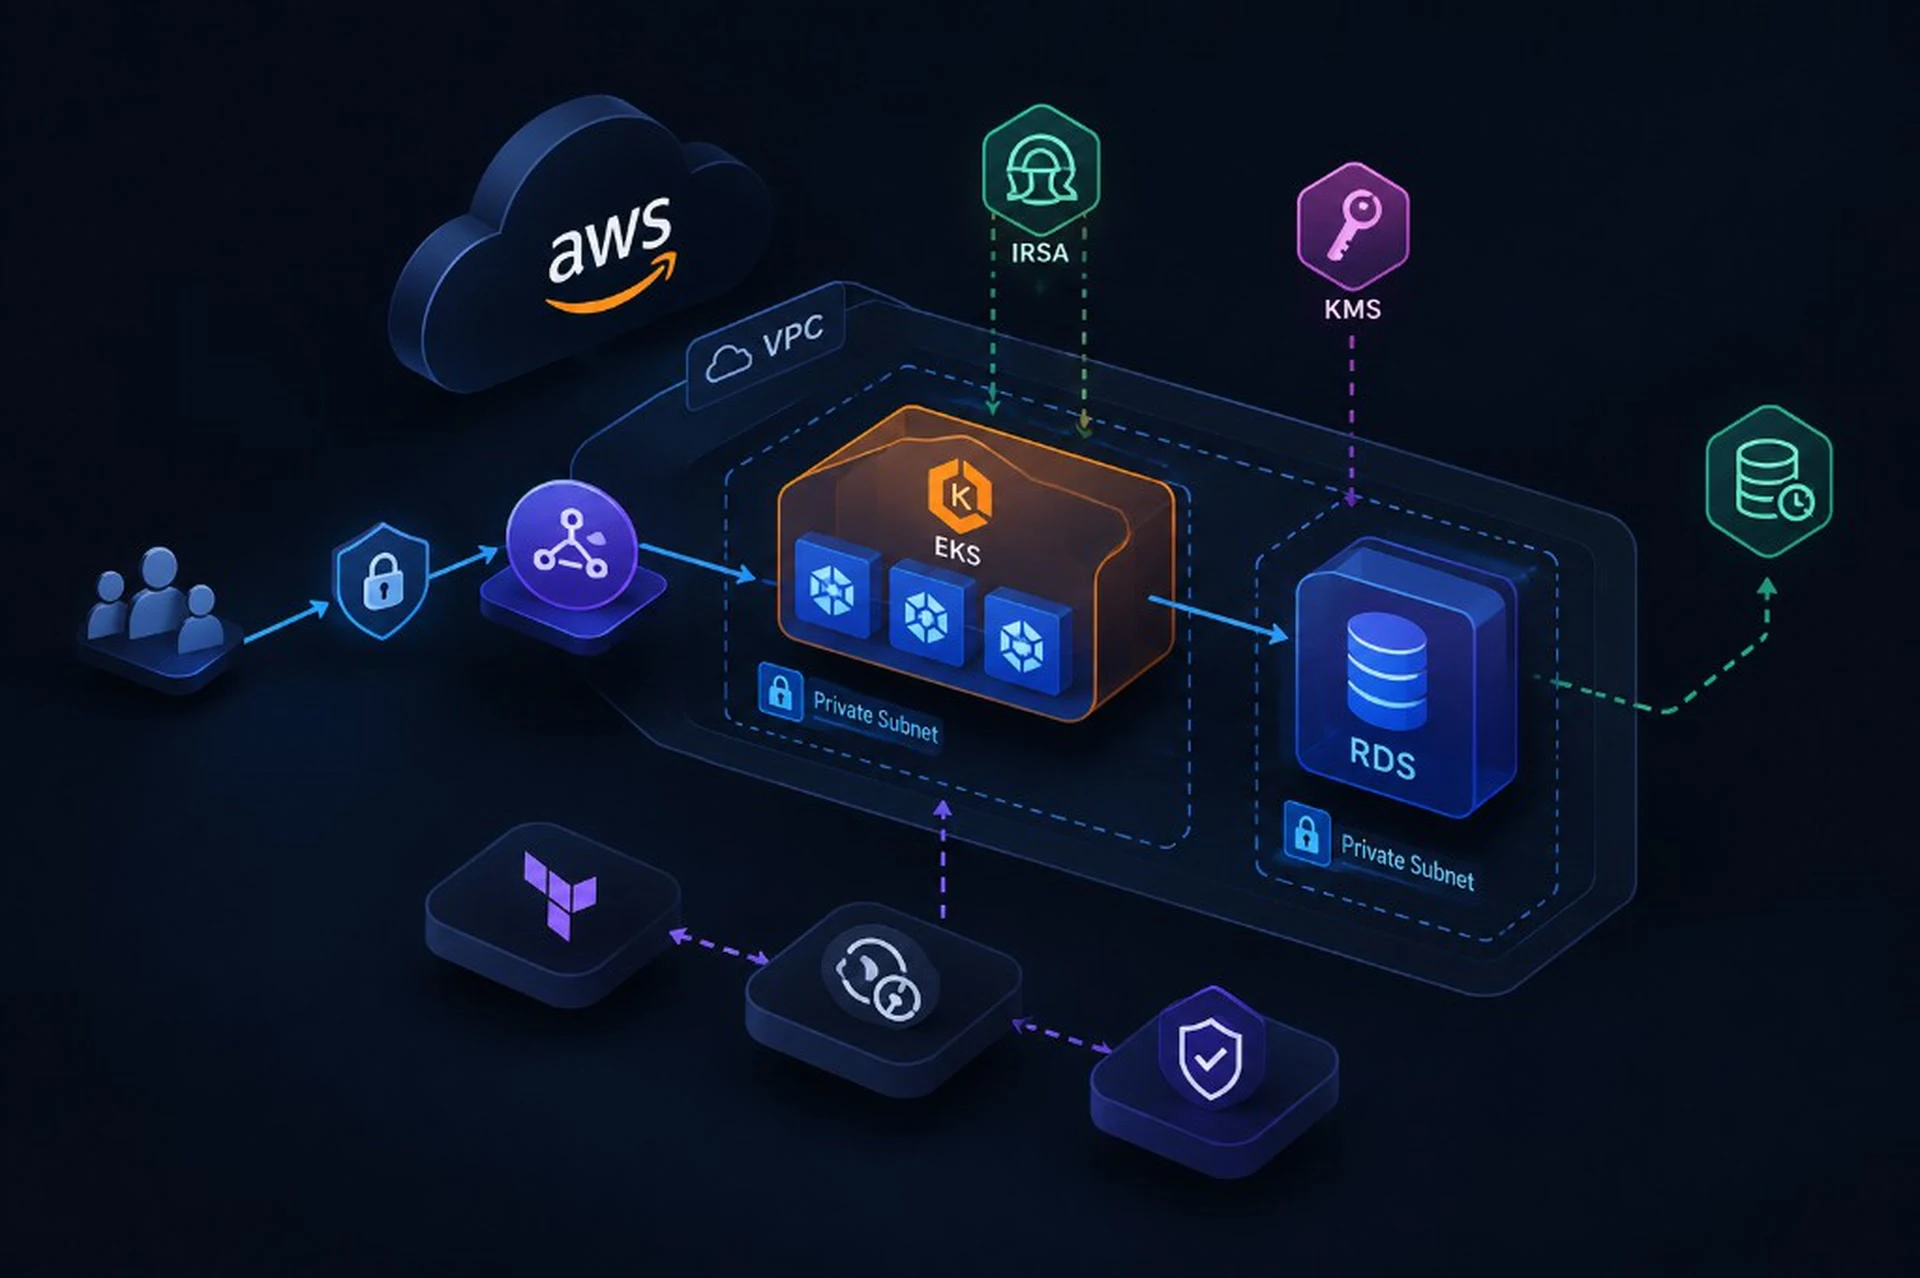
Single-account AWS app platform: private EKS + RDS behind a public ALB, with IRSA, KMS, backups, and policy-as-code CI.
Terraform · EKS · IRSA · Policy-as-code · OIDC
Runtime path
Internet → IGW → public ALB → private EKS → RDS. Private egress returns via NAT — never Internet → NAT.
01/06
VPC · 2–3 Availability Zones
Internet
Public clients and controlled outbound destinations.
Ingress starts here. There is no path Internet → NAT.
CI pipelines
Three real GitHub Actions workflows — validate, security scan, and human-gated OIDC plan.
fmt · init · validate across every module and environment root.
Stages
Checkout
Pinned actions/checkout — contents read only.
Terraform fmt
Recursive format check fails the PR on drift.
Validate roots
Explicit ROOTS list: modules, environments, and examples/full-stack.
Failure logs
Upload per-root logs when validation fails.
.github/workflows/terraform-validate.yml
1- name: Terraform fmt2 run: terraform fmt -check -recursive3 4- name: Validate roots5 run: |6 ROOTS=(7 modules/networking modules/security modules/storage8 modules/database modules/eks modules/alb modules/observability9 environments/dev environments/staging environments/prod10 examples/full-stack11 )12 for dir in "${ROOTS[@]}"; do13 (cd "$dir" && terraform init -backend=false && terraform validate)14 doneBuilt for real teams
Every claim maps to a file in the public repository — not a slide deck.
Private EKS API
Control plane endpoint is private-only — reach via VPN or SSM after apply.
Source · modules/eks/main.tfIRSA for add-ons
OIDC-federated roles for EBS CSI, Load Balancer Controller, and app service accounts.
Source · modules/eks/irsa.tfPer-service KMS CMKs
Separate keys for S3, RDS, EKS secrets, logs, CloudTrail, SNS, and Backup.
Source · modules/security/main.tfIsolated DB subnets
Database route tables have no IGW and no NAT — private only.
Source · modules/networking/main.tfPolicy-as-code CI
PR gates: fmt, TFLint, Trivy, Checkov, Conftest, OPA, and Gitleaks.
Source · .github/workflows/terraform-security.ymlManual OIDC plan
Human-gated terraform plan via GitHub OIDC — no long-lived AWS keys in CI.
Source · .github/workflows/terraform-plan.yml
Explore the modules
Select a module and a file. Curated snippets load when available; otherwise open the file on GitHub.
Modules
Files
Multi-AZ VPC with public, private application, and isolated database subnet tiers.
- modules
- networking
Why it matters: Database route tables intentionally omit 0.0.0.0/0 — no IGW, no NAT.
1resource "aws_route_table" "database" {2 count = length(aws_subnet.database)3 vpc_id = aws_vpc.this.id4 5 tags = merge(var.tags, {6 Name = "${var.name_prefix}-database-rt-${count.index}"7 })8}9 10# Database subnets intentionally have no default route to NAT/IGW.Control matrix
Encryption, secrets, identity, detection, and recovery — defaults for operable environments.
- Encryption
Per-service KMS CMKs across S3, RDS, EKS, logs, and more
Source · modules/security/main.tf- Secrets
RDS master password in Secrets Manager — never in tfvars
Source · modules/database/main.tf- Identity
OIDC provider + IRSA roles + EKS access entries
Source · modules/eks/irsa.tf- Detection
CloudTrail + Config (observability) and GuardDuty (security) — flag-gated in prod examples
Source · environments/prod/main.tf- Recovery
AWS Backup vault with daily RDS selection
Source · modules/observability/main.tf
Want something at this level?
Tell us what you are building — we will shape the path with you.